A false sense of security
After years of neglecting information security, many organisations now hire external consultants to test their applications. These consultants typically come in for a few days every year, test the web applications, produce a report, which is then acted upon, or not, and the matter is considered closed until the next year.
That typical black-box penetration test gives a false sense of security. Yes, it simulates a real attacker. It does not go deep enough. Why do consultants keep finding new issues in applications that have barely evolved? Why do some consultants find a lot more than others?
Our difference
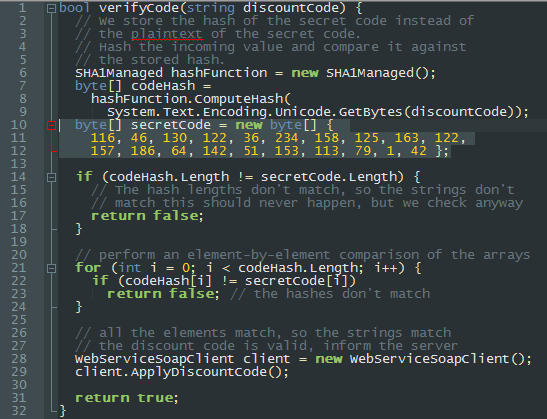
We specialise in white-box application testing and code review. We couple the typical hacker simulation with an in-depth review of your code using automated tools and manual checks. If there is a vulnerability in your application, we will find it, as we have in dozens of proprietary and commercial applications.
A typical security code review combined with a penetration test finds at least 50% more vulnerabilities than a penetration test alone.
Full confidence
Any confidential data given to us, including source code, is kept encrypted with current industry-standard algorithms and handled accordingly. After the engagement we wipe the data within 365 days. Our non-disclosure agreements are honoured in perpetuity.